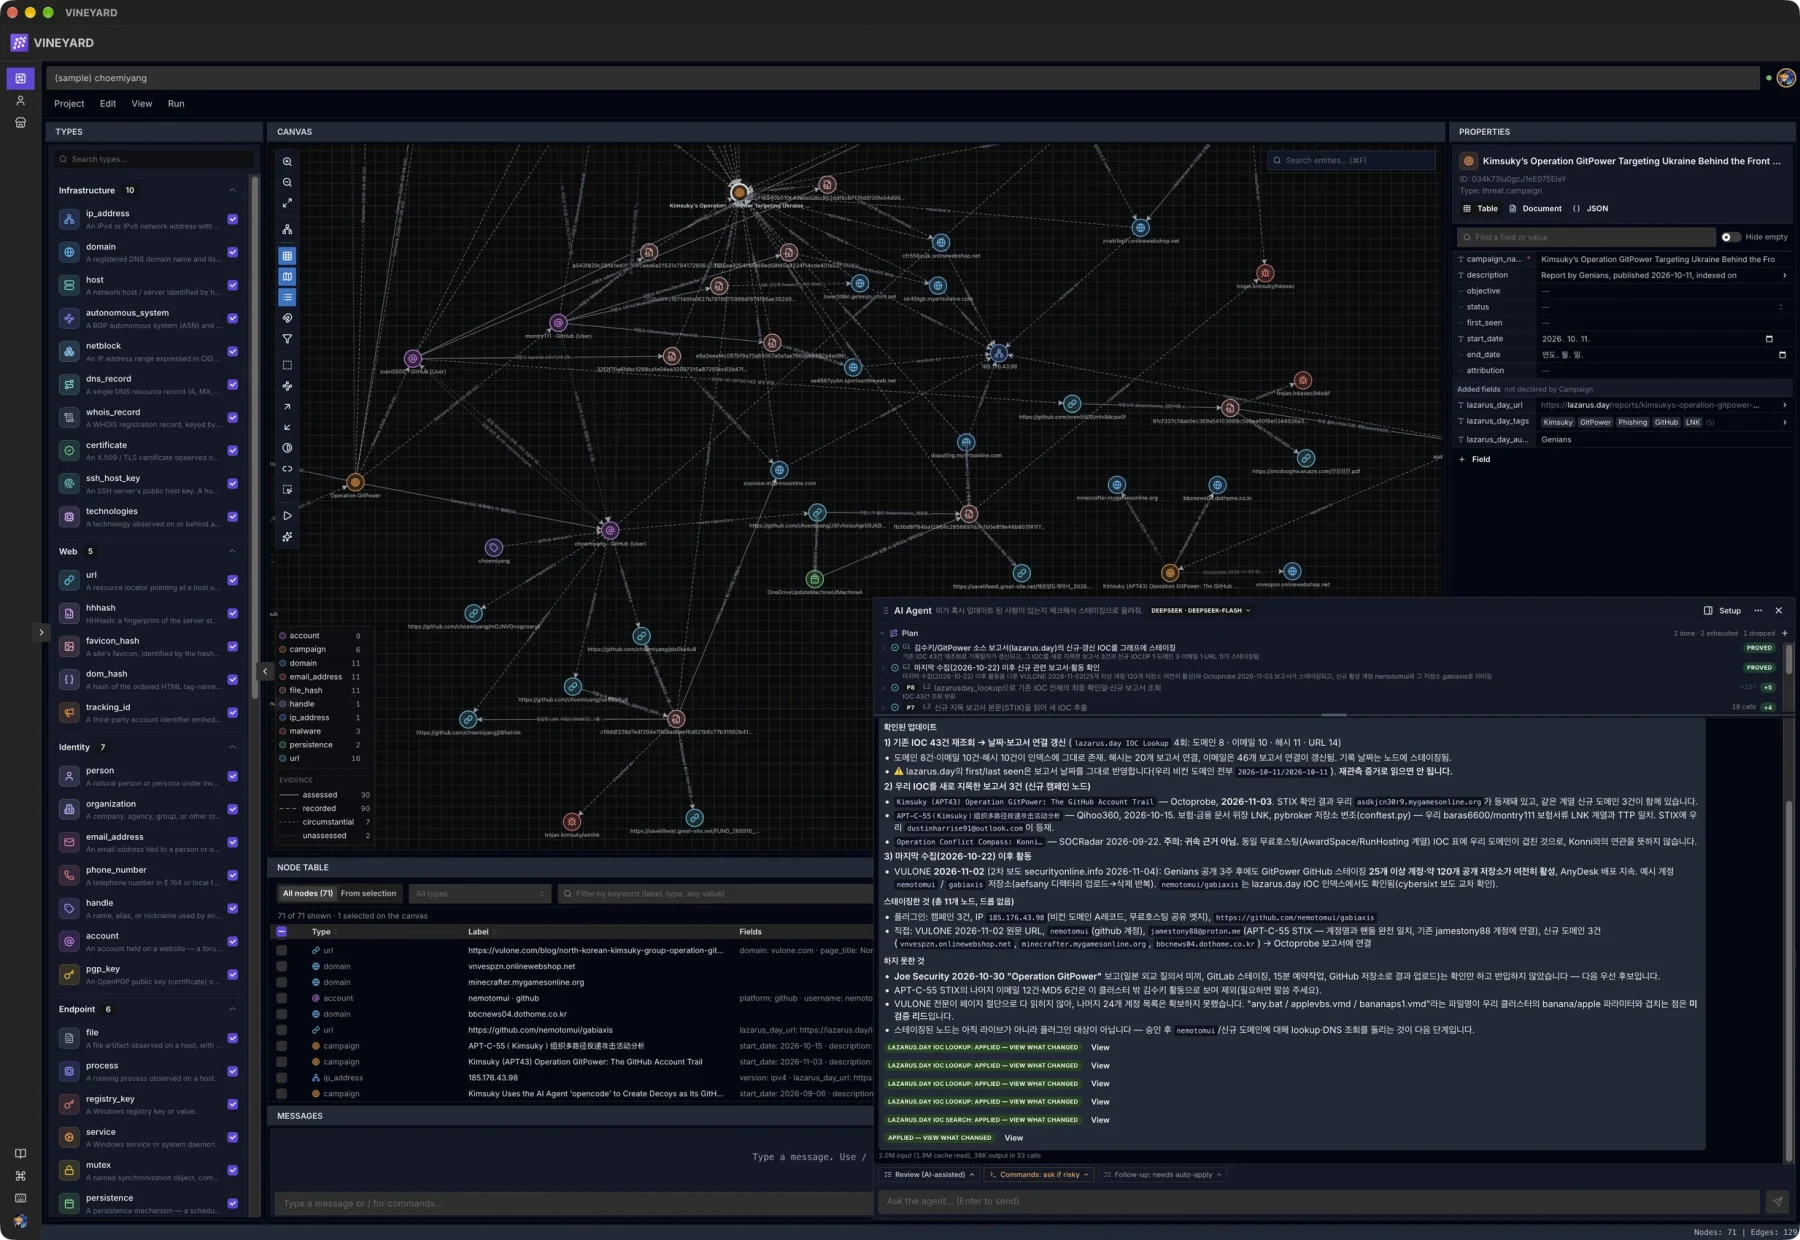
DIVE INTO THE SEA OF CYBER THREAT INTELLIGENCE |
VINEYARD empowers CTI analysts to accelerate investigations by revealing hidden relationships and turning fragmented threat intelligence into actionable insights.
> INSTALL DESKTOP CLIENT
✕
macOS
WINDOWS
LINUX
ONE COMMAND
curl -fsSL https://vineyard.run/install.sh | bash
COPY
HOMEBREW
brew install --cask Vineyard-Intelligence/ vineyard/vineyard
COPY
UNSIGNED BUILD. Opened from the .dmg, macOS refuses it the first time
("cannot be verified"): then System Settings → Privacy & Security
→ Open Anyway. The command above avoids this entirely.
UNSIGNED BUILD. SmartScreen will warn on first run:
More info → Run anyway.
ONE COMMAND
curl -fsSL https://vineyard.run/install.sh | bash
COPY
Picks the package for this machine — apt on Debian and Ubuntu, pacman
on Arch and Omarchy, an AppImage in ~/.local/bin on any other distribution
— and checks it against SHA256SUMS before installing.
OR DOWNLOAD A PACKAGE
The AppImage needs FUSE 2 (libfuse.so.2); the ARM64 one also needs libz.so
— zlib1g-dev on Debian and Ubuntu, already there on Arch. Checksums:
SHA256SUMS .
INSTALL A DOWNLOADED FILE
sudo apt install ./Vineyard-*.deb
COPY
sudo pacman -U ./Vineyard-*.pkg.tar.zst
COPY
chmod +x Vineyard-*.AppImage
COPY
Run in the folder the file was saved to. If that folder holds more
than one Vineyard file, type the full name of the one you want in
place of the Vineyard-* pattern. The AppImage needs no
install: once it is executable, start it by its name, e.g.
./Vineyard-linux-x86_64.AppImage , from wherever you keep it.
EARLY LINUX BUILD, unsigned like the others. So far it has been run on Ubuntu
24.04, Xubuntu and Omarchy only; the macOS and Windows builds are the tested
ones — please report what breaks. Korean text renders out of the box on
Ubuntu and Xubuntu; typing Korean needs an input method such as ibus-hangul .